Kategorien durchsuchen
Deutsch
$
USD
Deine KI mit Fiverr verbinden
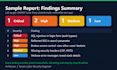
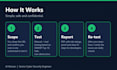
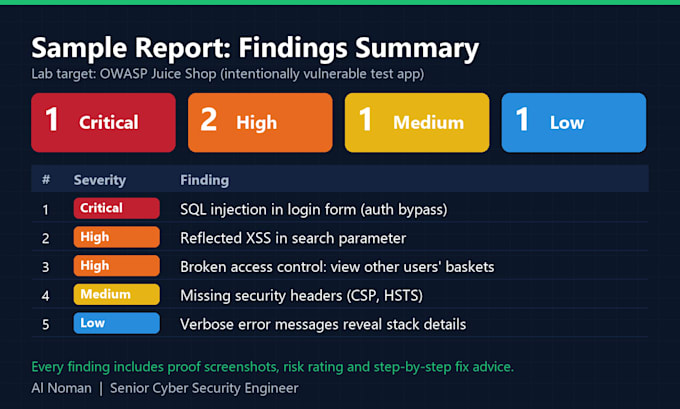
Worried your website or API has security holes? I will test it the way a real attacker would and give you a clear report your developers can act on.
I am a Senior Cyber Security Engineer running a live SOC. Every test is manual plus tool-assisted (Burp Suite, Nmap, Kali Linux), based on the OWASP Top 10.
What I check:
What you get:
Rules I follow:
Please message me before ordering so we can agree on scope and timing.
Bitte beachte, dass es gegen die Richtlinien von Fiverr verstößt, wenn Freelancer Themes, Vorlagen oder andere Elemente, die die Rechte Dritter oder geltende Gesetze verletzen, in die gelieferte Arbeit aufnehmen. Lies mehr darüber in unseren Leitfaden für verantwortungsvolle digitale Kreation.
Senior Cyber Security Engineer, VAPT and SOC Automation
Sprachen
Will the test break my website?
No. I use safe, non-destructive tests. I can also test a staging copy if you prefer.
Do you need my login details?
Only a test account, never your admin password. Please create a separate test user for me.
What if you find nothing critical?
You still get a full report showing what was tested and passed, which is useful proof for your clients and audits.
Do you fix the vulnerabilities?
I give clear fix steps for your developers. Fixing the code can be done as a separate custom offer.