Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD
Cybersecurity Specialist and Certified Ethical Hacker
Is your web application safe from cyber attacks, data leaks, and security flaws? Don't wait for hackers to exploit your business.
As a cybersecurity specialist, I deliver end-to-end Penetration Testing & Vulnerability Assessments (VAPT) to secure your web application and APIs.
What Is Covered:
Why Work With Me?
Packages:
Note: Target ownership or authorization required before testing.

Anwendung testen:
Web-Applikation
Entwicklungstechnologie:
JavaScript
•
Node.js
•
PHP
•
Python
•
SQL
Gerät:
PC
•
Mac
•
Linux
Will you hack a website or account without permission?
No. I strictly perform ethical penetration testing. Explicit written permission or proof of target ownership/authorization is strictly required before any security testing begins.
What do you need from me to get started?
I need your target URL/subdomain, defined testing scope (what to include/exclude), and staging/test account credentials if you purchased an authenticated testing package (Standard or Premium).
Can you white-label the security report with my company logo?
Yes. I can brand the final PDF report with your company or agency logo so you can present it directly to your clients, stakeholders, or investors.
Will the penetration testing cause downtime or break my website?
No. All tests are conducted using controlled, safe exploitation methods to avoid breaking live production environments. However, testing on a staging environment is always recommended if available.
Do you fix the vulnerabilities discovered during the pentest?
The report includes step-by-step developer remediation guides to patch every vulnerability found. If you require hands-on patching services, I can provide a custom offer based on the scope of fixes needed.
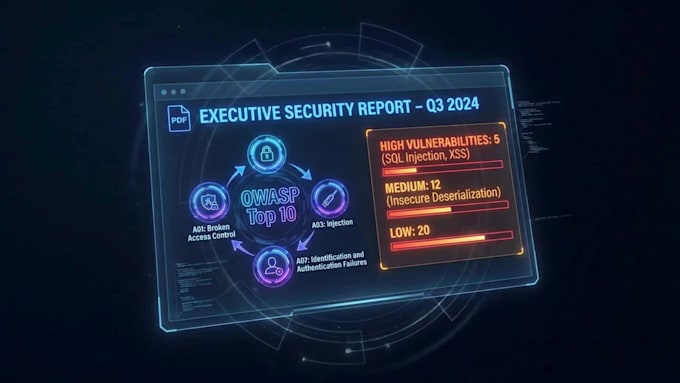
What format will the final deliverables be in?
You will receive an executive and technical PDF security report complete with risk ratings, Proof of Concept (PoC) screenshots/steps, and actionable fix guides. Premium orders also include an official Signed Security Certificate.