Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD
Penetration Testing And Web Security
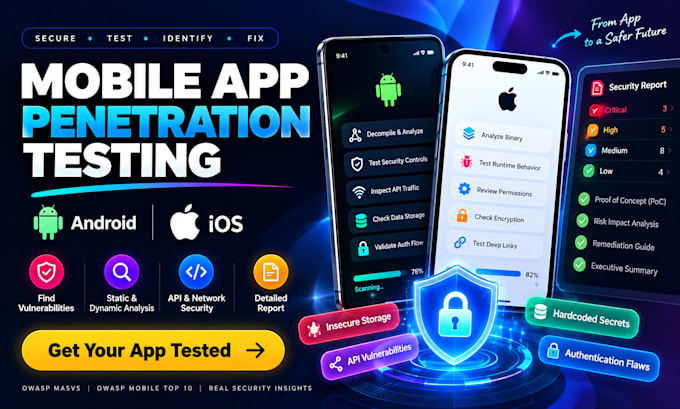
Is your Android or iOS app secure before launch, a major release, or a store submission?
I provide authorized mobile app penetration testing and security assessment focused on real vulnerabilities not just automated scanner output.
Depending on the package, I perform static and dynamic analysis of APK/IPA files, authentication and authorization testing, insecure data storage checks, API and network security testing, WebView and deep-link review, SSL/TLS and certificate-pinning checks, cryptography and binary protection review, and business-logic testing.
Testing can be aligned with OWASP MASVS/MASTG and the OWASP Mobile Top 10.
You receive a structured security report with vulnerability severity, affected components, evidence/PoC, impact, and clear remediation guidance.
Android, iOS, Flutter, React Native, and other mobile stacks can be assessed depending on access and scope.
Only authorized applications are tested. Message me before ordering for complex apps, source-code review, or deeper backend/API testing.
Cloud-Provider:
microsoft azure
Expertise:
Debuggen
•
Performance
Cloud-Computing-Ressource:
Route53
•
Security Groups
What do you need to start the mobile app security testing?
Please provide the APK or IPA, or an authorized store/download link, test credentials where applicable, and a brief description of the application. For API testing, provide the relevant API documentation, endpoints, or test environment details. You must also confirm that you own the application or h
Do you test both Android and iOS apps?
Yes. Android and iOS mobile application penetration testing are supported. Basic and Standard packages cover one platform, while Premium covers both platforms within the agreed scope.
Do I need to provide the source code?
No. A compiled APK or IPA is sufficient for black-box security testing. Source code is optional and can provide deeper coverage for code-level and grey-box security analysis. Current Fiverr mobile security sellers explicitly distinguish compiled-app testing from optional source-code access.
Do you perform both static and dynamic analysis?
Yes. Static analysis reviews the application package and configuration, while dynamic testing examines application behavior during runtime. The exact depth depends on the selected package.
Will you test the APIs used by my mobile application?
Relevant mobile API security checks can be included in the Standard and Premium packages. Full standalone API penetration testing, large API inventories, or extensive backend testing may require a custom offer.
Will I receive a security report?
Yes. You will receive a professional report containing confirmed findings, severity, affected components, technical evidence, impact, and practical remediation recommendations. Detailed reporting with evidence, severity and remediation is a recurring feature among current Fiverr mobile pentesting of
Can you test Flutter or React Native applications?
Yes. Mobile applications built with Flutter, React Native and other common frameworks can be assessed, provided the required build or runtime access is available.
Can you retest the application after vulnerabilities are fixed?
Yes. A remediation retest can be included in Premium or added separately to verify whether previously identified issues have been resolved.
Do you use automated security scanners?
Automated tools may be used for coverage, but important findings are manually reviewed and validated where applicable. The goal is to reduce false positives and provide actionable security findings rather than simply forwarding scanner output.
Can you guarantee that my application is completely secure?
No security assessment can guarantee that an application has zero vulnerabilities. Testing evaluates the agreed scope, environment and time period and aims to identify meaningful security weaknesses that should be addressed. That wording is also consistent with the more credible current Fiverr secur
