Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD


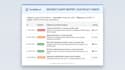
Your Lovable, Bolt.new, Replit, or Base44 app looks finished. It probably isn't secure. In January 2026, researched found 1 in 9 vibe-coded apps leaking Supabase credentials Api keys sitting exposed in the frontend bundle, Row level security never turned on. One misconfigured table and a stranger can read, write, or delete your entire database
I checked exactly that. I go through your lovable, Bolt, Base44 project looking for exposed service role keys, Missing RLS policies, hardcoded secrets, and broken auth, the mistakes AI coding tools make by default because they optimize for "it works" not "it's safe". You get a plain english reports for what exposed and why it matter. if you order a fix package, I Patch it directly in your supabase dashboard and codebase, test it, and hand back documentation you or your next developer can actually follow.
I won't pretend i can rebuild your whole app for $15. this is Scoped, Techical work, finding what actually broken and closing it before real user finds it for you.
Send me your project link and i'll tell you what i see before you order anything
I fix broken vibe coded apps fast honest no fluff
Sprachen
What tools do you support?
Lovable, Bolt.new, Bse44, v0, Replit, and Cursor projects, With a Supabase, Firebase, or postgres backend
will you fix bugs that arent security related?
Not on this gig I focus on security so i can do it properly. Message me if you also need feature work
Do you need my Supabase login?
Yes, read access at minimum to run the audit; I'll tell you exactly what access each tier needs before you order.
What if the audit finds nothing serious?
ou still get the full report most apps have at least a minor issue, but a clean scan is a real, useful result too.
Can you do this before I launch?
That's the ideal time cheaper and faster to fix than after real users are on it.