Kategorien durchsuchen
Deutsch
$
USD
Deine KI mit Fiverr verbinden
ALL IN ONE SOLUTION FOR BUSINESSES!!!
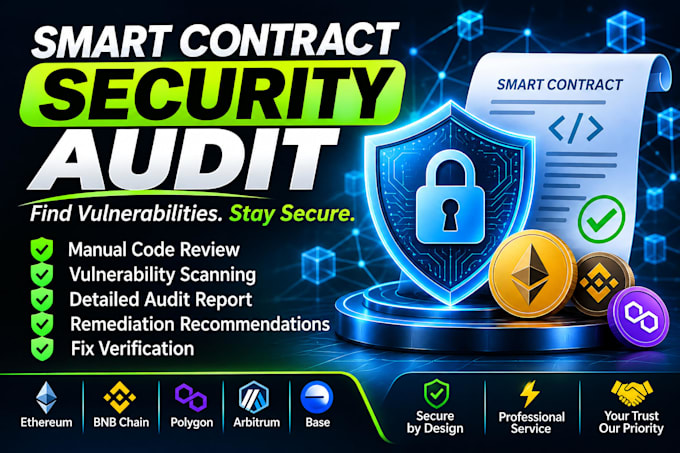
Launching an ERC20 or BEP20 token? Make security a priority before deployment.
I provide professional smart contract security audit services to help identify vulnerabilities, coding weaknesses and potential security risks in your token contracts.
What I audit:
What you'll receive:
Supported networks:
Ethereum, BNB Smart Chain, Polygon, Arbitrum, Base and other EVM-compatible networks.
Whether you're launching a new token or reviewing an existing contract, get your smart contract security assessed by a professional.
Contact me before ordering so I can review your contract complexity, requirements and recommend the right audit package.
Note: A security audit helps identify potential risks but cannot guarantee a completely vulnerability-free smart contract.
Tools:
MythX
•
Slither
•
Remix
Dienstleistungen im Bereich Kryptowährung konzentrieren sich ausschließlich auf die Entwicklung und Programmierung. Teile niemals vertrauliche Informationen oder private Schlüssel mit anderen.
What do you need to start the audit?
I’ll need your smart contract source code, deployed contract address (if available), target blockchain network, and any specific security concerns.
Which smart contracts do you audit?
I focus on ERC20 and BEP20 token smart contracts built with Solidity on Ethereum and other EVM-compatible networks.
Do you audit already deployed contracts?
Yes. I can assess both deployed and undeployed smart contracts, provided the source code and required access are available.
What vulnerabilities do you check for?
The assessment may cover reentrancy, access control flaws, unauthorized minting, integer issues, unsafe external calls, and other potential security weaknesses.
Will I receive a security audit report?
Yes. You’ll receive a PDF report outlining identified findings, their severity, and recommended remediation steps.
Do you fix vulnerabilities found during the audit?
The audit includes remediation recommendations. Actual code fixes are a separate service unless agreed upon before ordering.
Can you guarantee my smart contract will be 100% secure?
No. An audit helps identify potential vulnerabilities but cannot guarantee complete security. The report will document the findings within the agreed audit scope.