Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD
Cyber Essentials, Cyber Essentials Plus, ISO 27001, Web App Testing
Ill review your security policies against ISO/IEC 27001:2022, NIST CSF 2.0, the SOC 2 Trust Services Criteria or Cyber Essentials, whichever youre working towards, and show you exactly whats missing, whats too vague to follow and what to change.
I can review your cyber security policy, IT or acceptable use policy, and business continuity plan (checked against ISO 22301). Each document is reviewed section by section, from scope and ownership through to access control, patching, backups, incident response and supplier security.
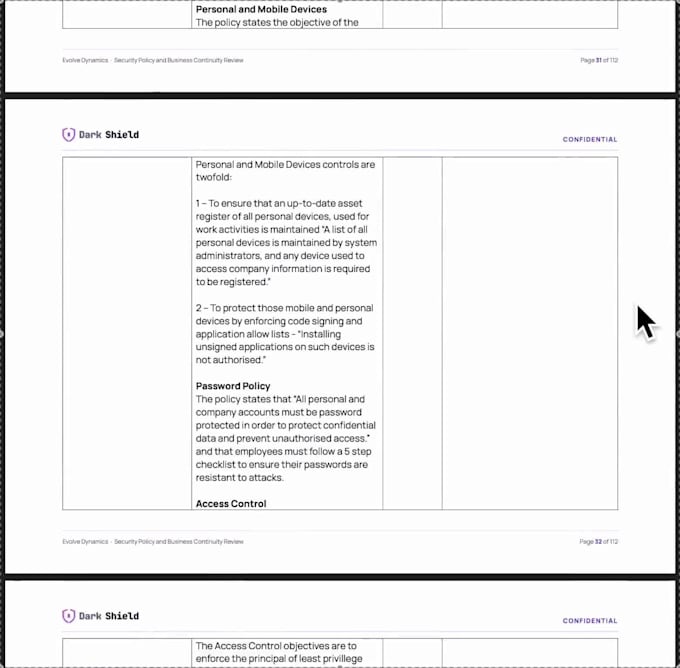
You get a written report with a short executive summary for directors, then a table for each document setting out what it says, where it falls short and a specific recommendation. Common findings include no named owner or review date, a scope that leaves out devices or cloud services, continuity plans that have never been tested, technical rules too vague to enforce, and documents that contradict each other.
Its a good first step before an ISO 27001 project, a SOC 2 audit, a Cyber Essentials assessment, a tender or a customer security questionnaire.



What framework should I choose to have my policy reviewed against?
Go with whatever your customer, tender or auditor asks for. As a rough guide, Cyber Essentials is common for UK government and supply-chain contracts, ISO 27001 is the international standard. If you’re not sure, we’ll decide on the discovery call.
Will this policy review make us compliant / certified?
No. The review checks your documents, not whether the controls are working in practice. Certifications are awarded from a licensed Certification Body. The review gets your policies ready for that step.
Can you rewrite our policies with the improvements?
The review tells you exactly what to change, with a specific recommendation for every gap, so your team can make the edits. If you’d like me to rewrite the documents or write missing ones, let me know and I can quote for it separately.
What happens if we are missing some policies?
That’s common and nothing to worry about. I’ll review what policies you have and, I'll list the documents your chosen framework expects that you don’t have yet, so you know what to write next. I can give support to write up any missing policies.
Are our documents kept confidential?
Yes. Your documents are only used for your review and aren’t shared with anyone. Send them through Fiverr rather than email, and I’m happy to sign an NDA before anything gets shared between us.