Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD
Freelance IT Auditor GRC Analyst
Need to evaluate vendor risk without reading 100-page SOC reports?
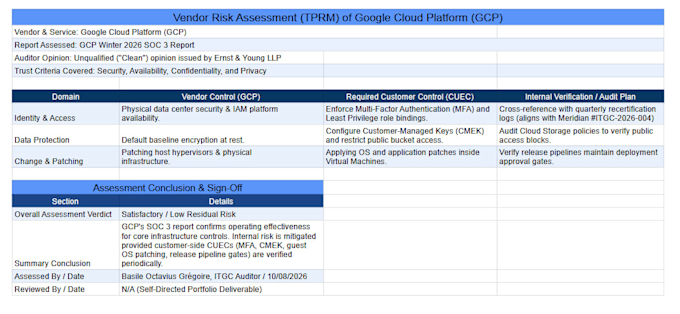
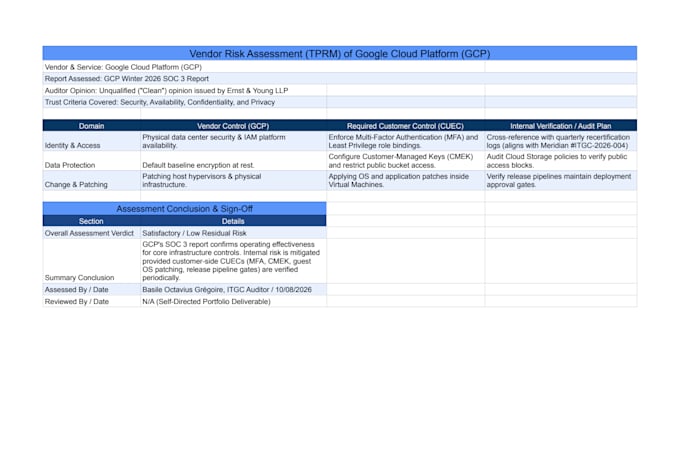
I analyze vendor SOC 1, SOC 2, and SOC 3 reports, extract Complementary User Entity Controls (CUECs), and build structured Third-Party Risk Management (TPRM) matrices to ensure vendor compliance.
What You Will Get:
Save hours of manual reading and get clean, audit-ready deliverables for your compliance audit.
Please message me before placing an order to discuss report formats!

What types of reports can you analyze?
I evaluate SOC 1 (Type I/II), SOC 2 (Type I/II), and SOC 3 reports across all Trust Services Criteria.
What format will I receive?
You will receive a structured Excel workbook (.xlsx) containing the TPRM CUEC mapping matrix and an executive PDF summary.