Kategorien durchsuchen
Entdecken
Fiverr Pro
Deutsch
$
USD
Artificial Intelligence and Software Engineer
Kompetenzen
Meine Dienstleistungen
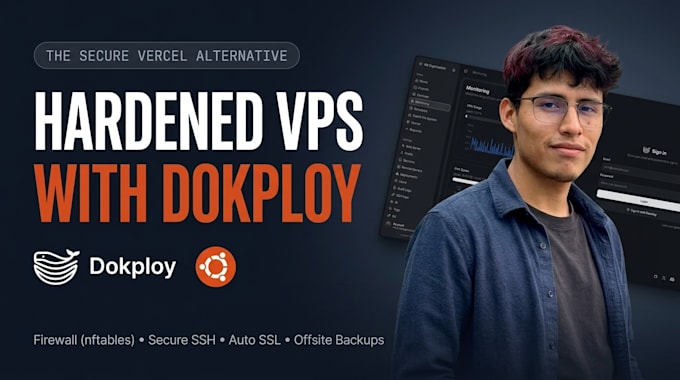

DevSecOps & Cloud Infrastructure Engineer
Fiverr • Freiberufler
Jan 2026 - Feb 2026 • 1 mo
Architected, deployed, and hardened production Linux VPS environments (Ubuntu 24.04 LTS) for self-hosted PaaS and containerized applications. Key Achievements & Responsibilities: • Custom Firewall & Network Engineering: Designed custom dual-stack (IPv4/IPv6) nftables rulesets with default-drop policies, SYN flood protection, packet validation, and kernel-level dynamic sets for automated SSH brute-force mitigation—preserving Docker bridge and overlay NAT networking without conflicts. • Server Hardening & Access Control: Enforced strict least-privilege security via SSH port migration, Ed25519 key-only authentication, root login prohibition, Docker socket isolation (660 permissions with empty docker group), and AppArmor enforcement. • PaaS & Container Orchestration: Deployed and managed Docker, Docker Swarm, and Dokploy with Traefik reverse proxy (HTTP/3 & automated Let's Encrypt SSL certificates). • Automated Disaster Recovery: Engineered daily encrypted backup pipelines to Cloudflare R2 (S3-compatible storage) using Restic and sandboxed systemd timers/services (DynamicUser, ProtectSystem=strict). • Security Auditing: Performed comprehensive read-only security audits analyzing open sockets, routing tables, sysctl kernel parameters, and automated security patching (unattended-upgrades).
