Kategorien durchsuchen
Deutsch
$
USD
Deine KI mit Fiverr verbinden
Cybersecurity Specialist, Web Security and Penetration Testing
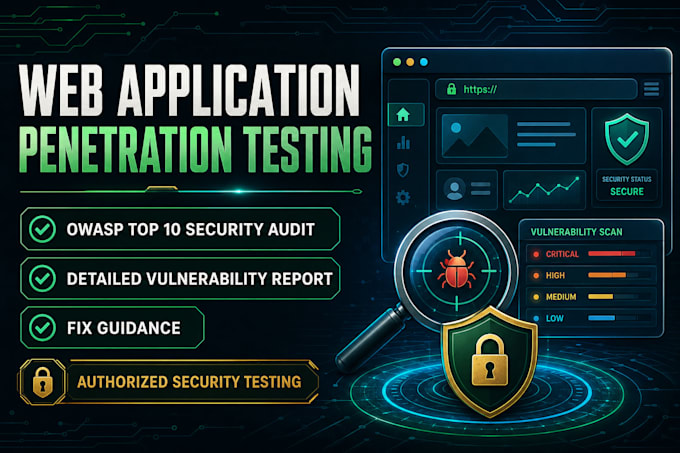
Welcome to my professional Web Application Penetration Testing and Vulnerability Assessment gig!
Are you concerned about the security of your web application? I will perform a comprehensive security audit and penetration test to identify vulnerabilities before hackers can exploit them.
What I Offer:
Why Choose Me?
Note: Please contact me before placing an order to discuss your project scope and specific security requirements.
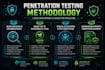
Gerät:
Desktop
•
Laptop
•
Server
•
Router
Betriebssysteme:
Windows
•
Linux
What do you need to get started?
I need your website URL/IP, written authorization/permission to test, and login credentials (if testing behind authentication).
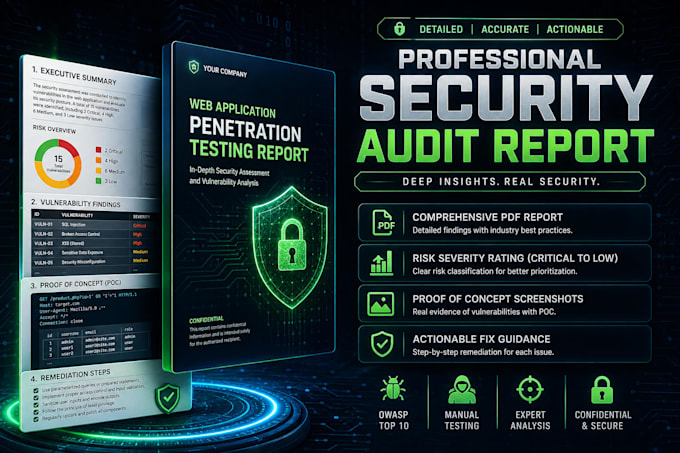
Will I receive a detailed security audit report?
Yes, you will receive a comprehensive PDF report detailing discovered vulnerabilities, severity levels, Proof of Concept (PoC), and recommended fixes.
Do you fix the discovered vulnerabilities?
I provide step-by-step remediation guidance in the report for your developer. If you need me to fix them directly, I offer fixing services starting from $30 (depending on complexity).
What do you need if I hire you to fix the vulnerabilities?
For fixing or patching, I will need temporary developer access, such as cPanel, FTP/SFTP, SSH, or source code repository access (GitHub/GitLab).
Will fixing or testing affect my live website?
I conduct penetration tests safely to avoid downtime. For fixing, I recommend providing a staging or test environment to patch code safely before updating your live site.